MaRisk AT 9 · AT 4.4.3 · DORA
Manage outsourcing traceably.
RegStack maps the MaRisk requirements for outsourcing management at leasing and factoring companies into one continuous process: from the materiality assessment through contract review and service provider management to the report to the management board. Every change is logged with the person and the time and remains traceable for internal and external audits.
Outsourcing management available in German and English.
Automation of regulatory workflows
Review, documentation and reporting processes run through defined workflows in all modules, with clear responsibilities, deadline reminders and escalation when something is left undone. Finished reports go to the management board for acknowledgement.
Management dashboard for regulatory status
One view shows where the institution stands: open decisions, running deadlines and open findings across all modules.
Audit-ready data
Every decision is recorded in a structured way, with its justification. Auditors receive read-only, logged access to the approved data.
01 · Outsourcing management
From materiality to the report. In one system.
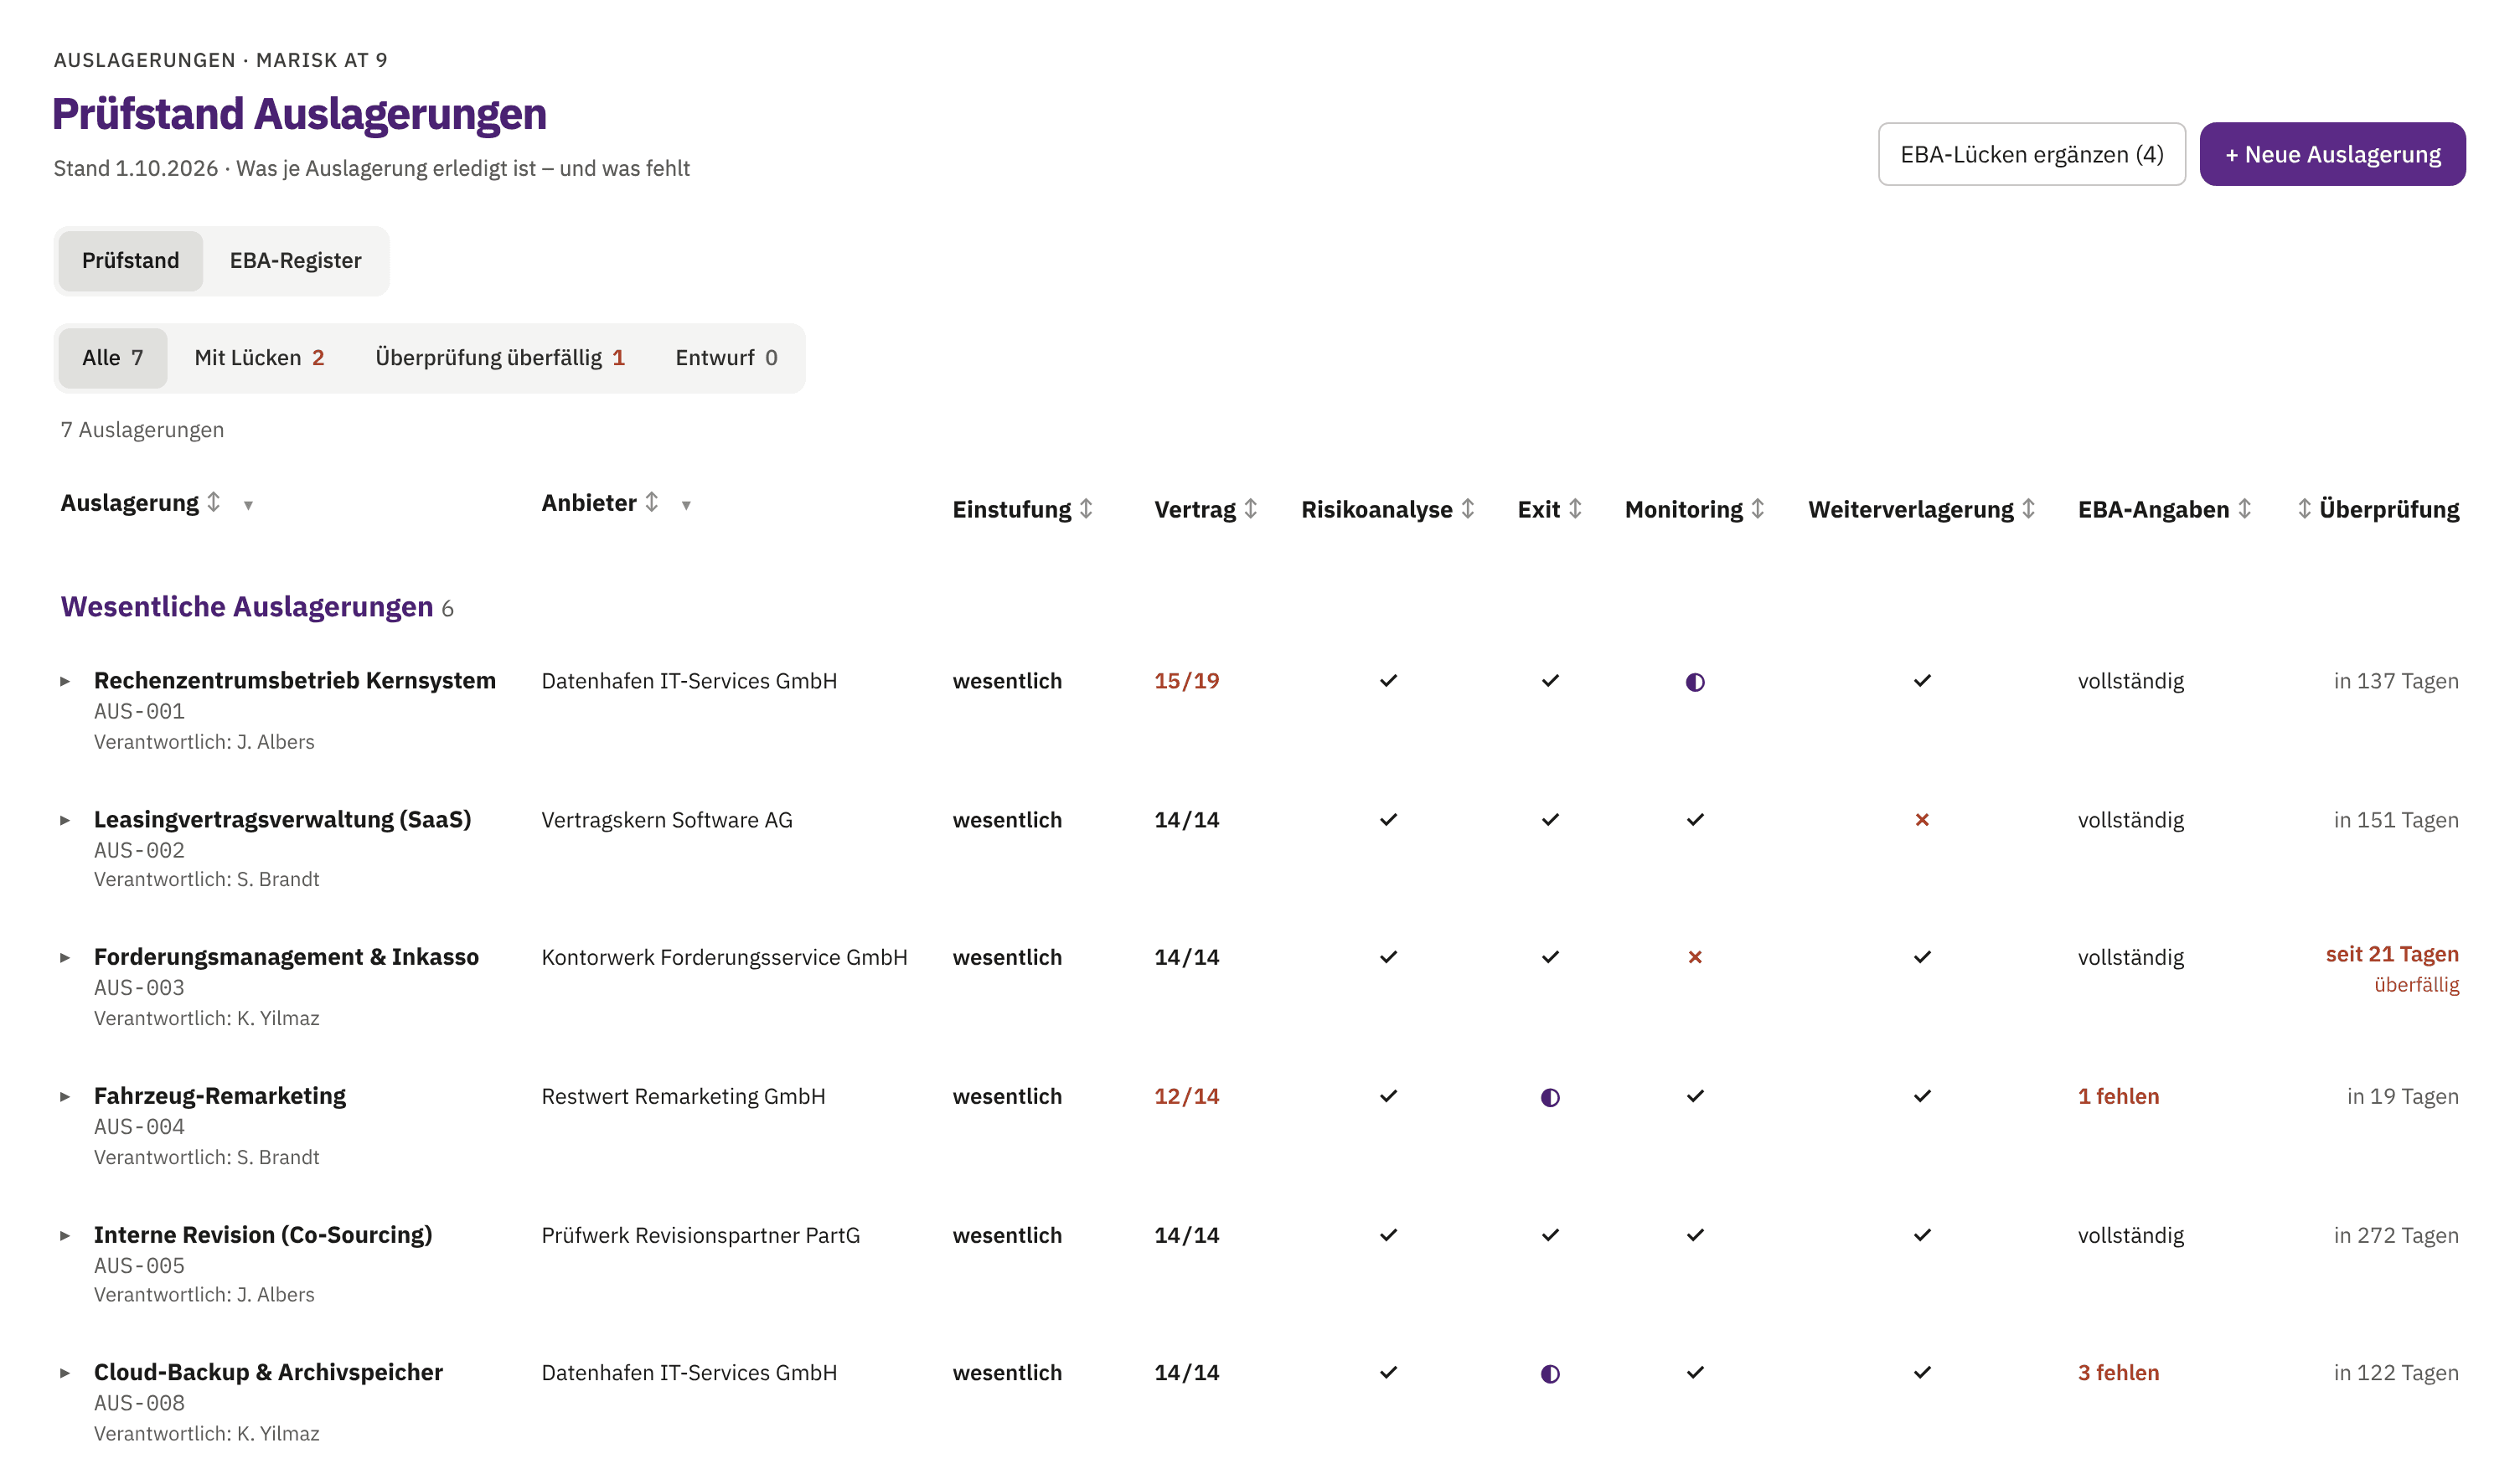
Every outsourcing arrangement has its own page: classification with justification, contract, monitoring and next review. Anything missing or soon due is visible in the register before the supervisor asks for it.
- para. 2
- Materiality model includedYou do not need to build your own model. RegStack provides a quick check, criteria and thresholds; if you wish, the business unit assesses individual criteria directly in the system. The result follows from the quick check and the criteria; a hard trigger always leads to “material”.
- para. 4 / 5 / 10
- Active only once completeAn outsourcing arrangement only becomes “active” once the mandatory AT 9 information has been recorded, for material arrangements for example the verified authorisation of the service provider.
- Risk
- Risk analysis with deadlinesRegular reviews are scheduled with due dates. The register counts overdue analyses and expiring contracts, and one click filters them out.
- Monitoring
- Monitoring service providersKPI and SLA values, exit strategy and sub-outsourcing for each outsourcing arrangement.
- para. 13
- Outsourcing report preparedRegStack drafts the mandatory statements from the financial year’s data. You review and complete them; the PDF is generated with a frozen state of evidence.
- DE | EN
- Also in EnglishThe outsourcing management interface can be switched to English, using the terminology of the EBA Guidelines. Reports and exports for supervisors and auditors remain in German.
- DORA
- DORA register of information available, module under developmentThe register of information records ICT third-party service providers and contracts field by field under the ITS 2024/2956 and is linked to the outsourcing arrangements in the register. The rest of the DORA module is still under development.
New · EBA/GL/2019/02 paras. 54–56
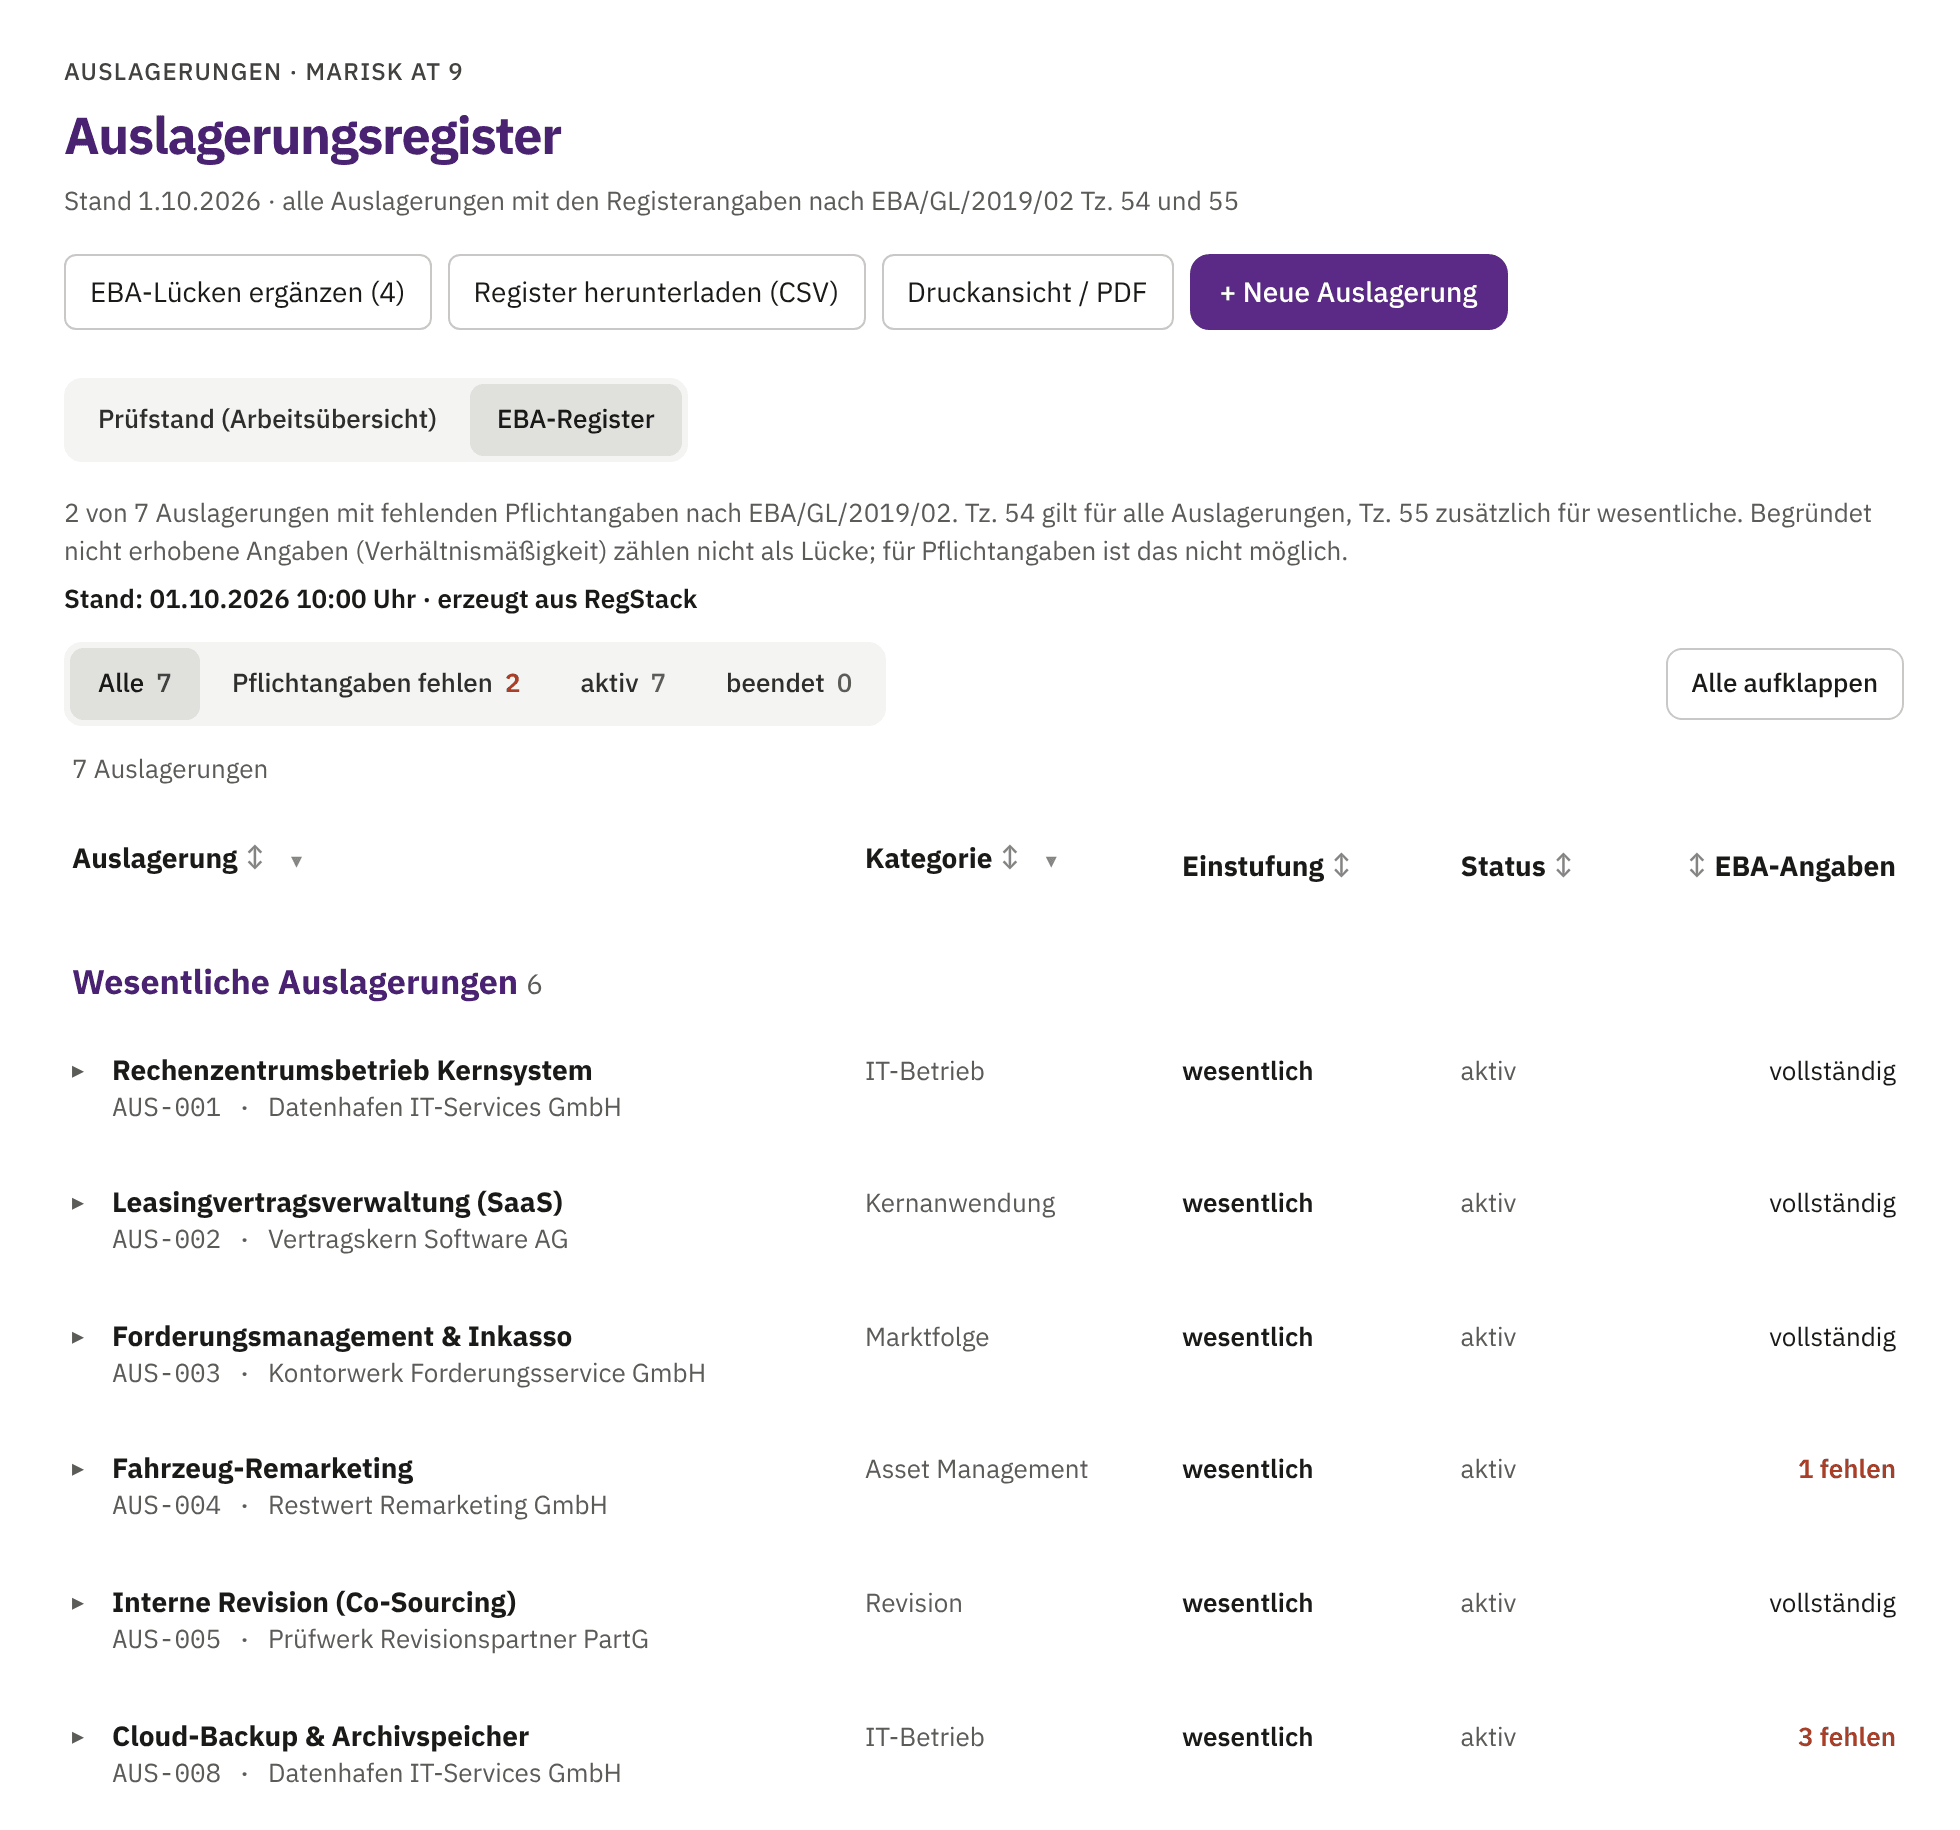
The outsourcing register under the EBA Guidelines.
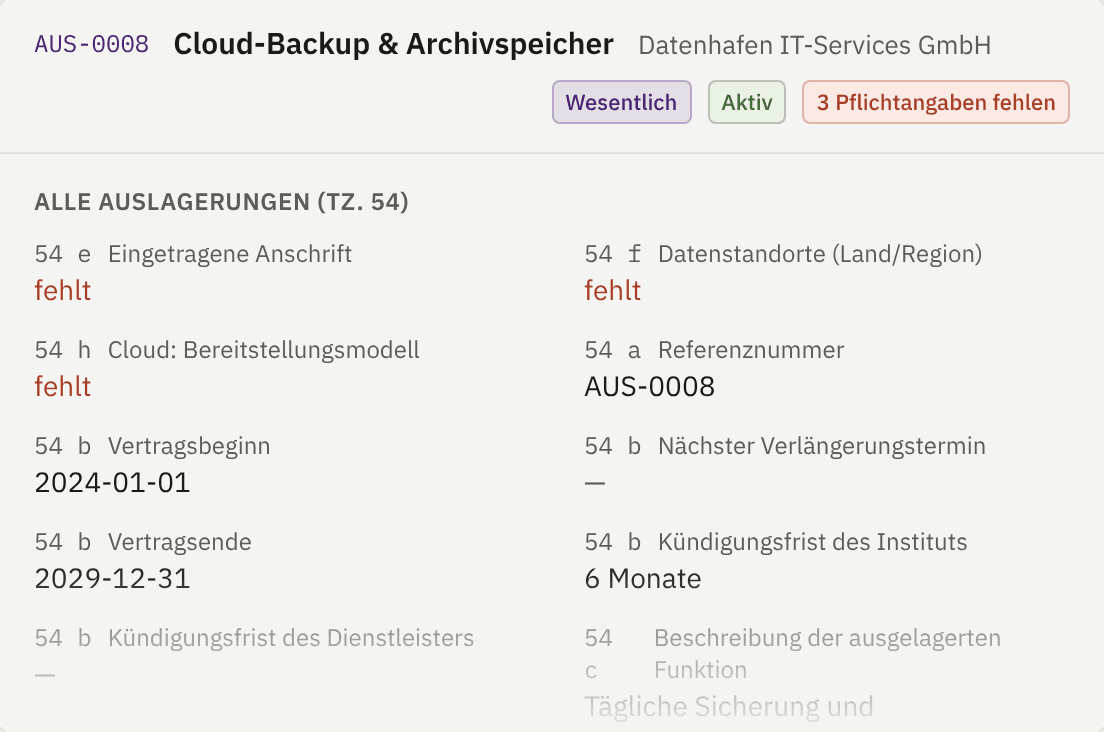
Every item of information required by the EBA Guidelines has its own field: para. 54 for all outsourcing arrangements, para. 55 additionally for material ones. Anything missing is visible at once.
- 54 a–iInformation for all outsourcing arrangementsAutomatic reference number, terms and notice periods, data and data locations, service providers with registration number and address, cloud models.
- 55 a–kMaterial outsourcing arrangements in detailApproval, governing law, subcontractors, substitutability, alternative providers, estimated annual cost.
- GapsMissing mandatory information flaggedCounted for each outsourcing arrangement and highlighted in red, not only once the audit begins.
- para. 56Information for the supervisor as CSVRegister with all EBA information and a review status overview, optionally filtered by category.
02 · Internal audit
The paragraphs of AT 4.4.3, translated into functions.
Which function covers which paragraph is set out in the system description in the product and can be checked against the MaRisk text. Internal audit’s evidence is created in the course of ongoing audit work.
- para. 1 / 2
- Independence of internal audit
- Regular declaration of independence by the head of internal audit, with a set cycle and deadline alerts.
- para. 3 / 4
- No self-review, cooling-off period
- Cooling-off periods for staff moving into internal audit and a self-review questionnaire for every auditor.
- para. 5
- Coverage of the audit universe
- Coverage check across all four areas. Outsourced activities without an audit object are shown as a gap.
- para. 6
- Risk-based planning
- Each audit object is assessed against four criteria. The history remains unaltered.
- para. 8 / 9 / 12
- Defined escalation
- Severe findings are escalated to the management board automatically. If a finding concerns a member of the management board, RegStack tracks the report to BaFin and Bundesbank with deadlines; the institution submits the report itself.
Follow-up · para. 11
A finding remains open until the measure has demonstrably taken effect.
Nothing is closed without the result “effective”. If the follow-up is waived, the head of internal audit must give a written justification. Whether minor findings may be closed without follow-up is a one-off decision of the institution.
- 01Finding recordedWith severity, responsible person and deadline.
- 02Measure reported as completedThe business unit provides evidence of implementation.
- 03Follow-up dueStandard period of 30 days, configurable.
- 04Closed once effectiveIf rated “not effective”, the finding remains open.
03 · Compliance
Regulatory inventory, findings and reports in one place.
Evidence and monitoring for each assigned requirement. Auditors receive narrowly scoped read access, and every access is logged. View the compliance demo →
In detail
What the three core statements mean in day-to-day work.
Automation of regulatory workflows
- No more spreadsheets
- Registers, deadlines, evidence and decisions are managed in the system instead of spreadsheets, emails and file shares. One system for all governance functions instead of a stand-alone solution per department.
- Reports are generated automatically
- The outsourcing report and the internal audit and compliance reports are drafted from the recorded data. You review and complete them; the PDF is generated with a frozen state of evidence. The report then goes to the management board, which acknowledges it digitally.
- Deadlines and escalation
- Reviews, follow-ups and reports are scheduled and flagged in good time. Anything left undone is escalated.
Management dashboard for regulatory status
- Where the institution stands
- Which material outsourcing arrangements are running, which risk analyses and contracts are open, which deadlines are about to slip and where things are stuck, without chasing the departments.
- Decisions for the management board
- What the management board has to decide or note is shown separately from all other tasks. Every role starts in its own overview.
Audit-ready data
- Auditor access
- Access is limited to a period and to selected modules and can be revoked at any time. It is read-only, and every access is logged.
- Read-only view for auditors
- Auditors see the approved data in a dedicated read-only view and retrieve what they need. The institution no longer has to supply documents.
- Export from all modules
- Registers, evidence and audit documents can be exported from the individual modules, filtered and sorted as in the view, as CSV or PDF.
Further modules
RegStack covers further areas of the institution. We walk through scope and maturity in the demo.
- Internal control system
- Processes, controls and control matrix.
- Accounting
- Balance sheet, income statement, notes and management report with immutable versions.
- Risk management
- Risk inventory, risk-bearing capacity and reports under MaRisk AT 4.
- DORA module (in preparation)
- Register of information under Art. 28 DORA available, further functions under development.
About us
RegStack is built on audit and compliance experience from several regulated institutions. We know the requirements, media breaks and audit processes that RegStack addresses from our own practice.
Vendor assessment
Documents for your assessment under AT 9 and DORA.
Our vendor package is available on request: company profile, sub-processors and data residency, technical and organisational measures, backup and contingency planning, audit, exit and incident processes.
Request documentsSee RegStack with an example from your own institution.
In a 30-minute demonstration we walk through RegStack using one of your service providers, from the materiality classification to the outsourcing report.